Find Vulnerabilities Before Attackers Exploit Them

Penetration Tests for Your Business: Take an Offensive Approach to IT Security

As IT risks grow, especially from AI-driven cyberattacks, it is essential for organizations to take a proactive approach to IT security. A penetration test, often shortened to pentest, is a targeted IT security assessment in which professionals look for exploitable vulnerabilities in applications, systems, and infrastructure under controlled conditions. Our certified experts have already conducted more than 1,500 penetration tests. We provide more than just findings: we give you a sound basis for making decisions and allocating your resources effectively.

Schedule an initial consultation for a penetration test


Why You Should Strengthen Your Cybersecurity with Penetration Tests

From regulatory requirements and complex IT landscapes to rising expectations from business partners: There are many good reasons to regularly assess your security posture with a penetration test.


Meet Regulatory Requirements
Legislation such as NIS2 sets specific requirements for risk management and cybersecurity. Penetration tests can help assess security measures and document risks clearly.

Effective Risk Management
A vulnerability on its own does not reveal the actual risk to your organization. Penetration tests show which vulnerabilities are exploitable, which attack paths they enable, and which systems are actually affected. This helps you make informed assessments of security risks and identify targeted measures.

Uncover Internal Attack Paths
Vulnerabilities in internal environments, such as misconfigurations or incorrect permissions, pose a security risk. Controlled attack scenarios show which attack paths are actually exploitable and where targeted countermeasures should be applied.

Strengthen Trust with Business Partners
Business partners such as customers or service providers expect verifiable statements about your security posture. Oversights can cost you valuable business relationships. Address potential security vulnerabilities and strengthen your business partners' trust.

Penetration Testing Services for Different Attack Surfaces

As an experienced penetration testing provider, we tailor every penetration test precisely to the specific asset. Drawing on our roots in the highly regulated aviation industry and more than 1,500 successfully completed penetration tests, we have developed tried-and-tested processes that meet the requirements of each engagement. Our Focus Areas:
AI Applications

Evolving technology also brings new requirements for IT security. Keep pace with developments and use a penetration test to assess your AI applications for vulnerabilities.

Cloud & Hybrid Cloud

Test your cloud and hybrid cloud environments for security flaws that attackers could exploit.

SAP

SAP systems keep essential business processes running. Ensure that your SAP system landscape does not provide an entry point for cyberattacks.

Industrial Control Systems (ICS)

A penetration test of industrial control systems identifies vulnerabilities in critical environments and helps reduce outages, production interruptions, and security risks.

Additional penetration testing areas:

  • Mobile applications
  • Web applications
  • API
  • Client
  • Active Directory
  • Internet of Things (IoT)/operational technology (OT)
  • Infrastructure

Feel free to contact us:

Schedule an initial consultation for a penetration test 

In addition to penetration tests, we offer other offensive security services:

  • Vulnerability Scanning: Automatically scan assets for known vulnerabilities
  • Red Teaming: Simulation of a real cyberattack (this simulation may also include a penetration test)
  • Cloud Audit: Assessment of the cloud environment provided by your cloud service provider
Benefits of a Penetration Test
  • Identify and remediate security flaws early
  • Avoid the downstream costs of cyberattacks
  • Meet regulatory requirements
  • Protect reputation and customer trust
  • Assess the effectiveness of existing security measures
AI Penetration Testing: What Is an AI Penetration Test?

The term AI penetration testing covers both penetration testing of AI systems and the use of AI in penetration testing itself.

  1. In the first scenario, we assess, among other things, whether the security rules and the ethical or functional safeguards of AI applications can be bypassed, whether the model discloses training data or confidential data, or whether connected systems can be invoked without proper controls. A penetration test not only increases the security of AI systems, but also helps meet regulatory requirements under the EU AI Act.
  2. In the second case, AI supports penetration testing by guiding targeted attack simulations and helping uncover additional vulnerabilities.

How Does a Penetration Test Work?

A well-defined workflow reduces coordination overhead and provides assurance throughout the process. The penetration test with Lufthansa Industry Solutions (LHIND) is conducted in five steps:

Together, we agree on objectives, scope, and the technical and organizational parameters.

We verify approvals and access so the penetration test can start as planned.

Our experts perform manual testing, supplement it with automated checks, and verify the relevant findings.

We prioritize the findings, document them clearly for management and business units, and include specific remediation measures.

After remediation, we retest the findings and confirm whether the implemented measures are effective.

Your Outcome: A Sound Basis for Decision-Making

Once the penetration test is complete, you will receive more than just a list of vulnerabilities. We assess technical findings in their specific business context and turn them into clear, actionable recommendations—so you can quickly see what really matters, who needs to act, and which measures to prioritize.


You will receive:

Management Summary

An assessment of risks and their interplay so you can make decisions quickly and efficiently

Technical Findings

Relevant vulnerabilities are clearly described, substantiated with clear technical evidence, and mapped to the systems and areas actually affected.

Prioritized Measures

We translate findings into specific actions, prioritize them by impact, and establish a clear order for remediation.

Export of Results for Your Ticketing Tool

In addition to the report, you can optionally receive the results in a machine-readable format for further processing in your standard ticketing tool.

Lufthansa Industry Solutions: Aviation-Grade Security

Our close ties to the aviation industry give us in-depth knowledge of stringent security standards and experience working in highly regulated environments. We apply our experience from this demanding field to other industries and companies.

What you get from us:

  • Experience from more than 1,500 completed penetration tests
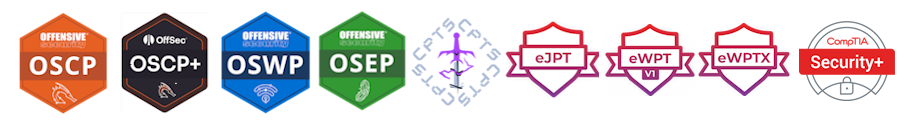
  • certified experts (with certifications including OSCP, OSEP, and eWPTX)
  • professional penetration tests based on internationally recognized penetration testing standards (in particular PTES, WSTG, and the OWASP Top 10)
  • a single point of contact and clear coordination processes
  • a reliable picture of your risks and prioritized findings rather than unverified scanner results
  • a clear, well-substantiated basis for management and business units to make decisions
  • Certified compliance with security and quality standards (ISO 27001, ISO 9001, ISO 14001, TISAX)

Certifications in Our Team

In-House Tools for Penetration Testing

Our experience shows that the tools available on the market cannot fully address current challenges. That's why we have developed our own tools that support our work and deliver even better results for you:

  • Specter & Black Halo – our solutions for intelligent testing of AI applications. In addition to technical testing, we also analyze business use cases and erroneous decisions.
  • ZeroBlue provides a simple, secure connection between your network and ours, creating the technical foundation for a smooth penetration test.


Frequently Asked Questions about Penetration Testing

During a penetration test, applications, systems, and IT infrastructure are systematically assessed for exploitable vulnerabilities and realistic attack paths. Experienced cybersecurity specialists conduct controlled attacks, verify relevant findings, and assess their potential business impact. Based on the technical risks, the experts derive specific courses of action for business units and management and propose prioritized measures.

A vulnerability scan is largely automated and identifies vulnerabilities, whereas a penetration test focuses on manual analysis within a clearly defined scope. The goal is to verify vulnerabilities, evaluate real attack paths, and determine their real-world relevance. When the goal is also to test how people, processes, and technical systems work together under realistic attack conditions, red teaming is typically used as a comprehensive, interdisciplinary attack simulation.

Automated tools are typically part of modern penetration tests—what matters is not whether they are used, but how. A reputable penetration testing provider combines automated scans and AI-powered tools with manual analysis: Penetration testers verify the findings, assess real-world attack paths, and retain technical accountability. This is evident from a well-documented presentation of evidence in the final report, a clear assessment of the risks and an optional results presentation. This allows you to determine whether vulnerabilities were actually tested or you are simply looking at unverified scanner results.


Relevant selection criteria include experience conducting penetration tests, as well as the qualifications of the experts involved. These qualifications can be demonstrated through hands-on professional certifications such as OSCP, OSWP, or OSEP. In addition, work should follow standardized frameworks, since they promote a structured approach and yield transparent, verifiable results. Equally important are transparency regarding the manual component of the penetration test and clear documentation of the approach, findings, and recommendations.

Would you like to learn more about a penetration test with LHIND?

Contact us now with your questions about offensive security measures – we’ll be happy to advise you.

captcha